One study found that off-store app campaigns can steal credentials from millions of users in weeks. That scale makes a single install far more dangerous than most people expect.
An Android Package Kit (APK) is the file format that delivers an application to your device. It holds code, resources, and assets that let an app run. Attackers exploit that format to hide payloads and tamper headers so tools miss them.
Real campaigns impersonate major brands, abuse permissions, encrypt command-and-control configs, and even block SMS to hide bank alerts. These threats use social engineering and third-party sources to push apps outside the Play Store.
This guide maps how a compromised file lands, what it does post-install, and practical defenses. We explain why installing unknown files opens your device to ad fraud, credential theft, covert control, and data exfiltration. Learn how to verify publishers, lock down sideloading, and spot telemetry that signals an active cyber threat.
Key Takeaways
- Understand the attack chain: how an android package kit can be weaponized after install.
- Watch permissions and telemetry: abused access and encrypted C2 are common hallmarks.
- Prefer trusted stores: Play Store protections reduce exposure compared with off-market sources — learn more here.
- Detect early: look for odd network beacons and altered file headers during triage.
- Defend practically: verify publishers, restrict sideloading, and monitor mixed fleets and BYOD devices.
Understanding APK Files and the Android Package Kit Format
The android package kit is a ZIP-style container that delivers an application to the operating system. It bundles executable code, resources, and a manifest that declares what the app can access and run.
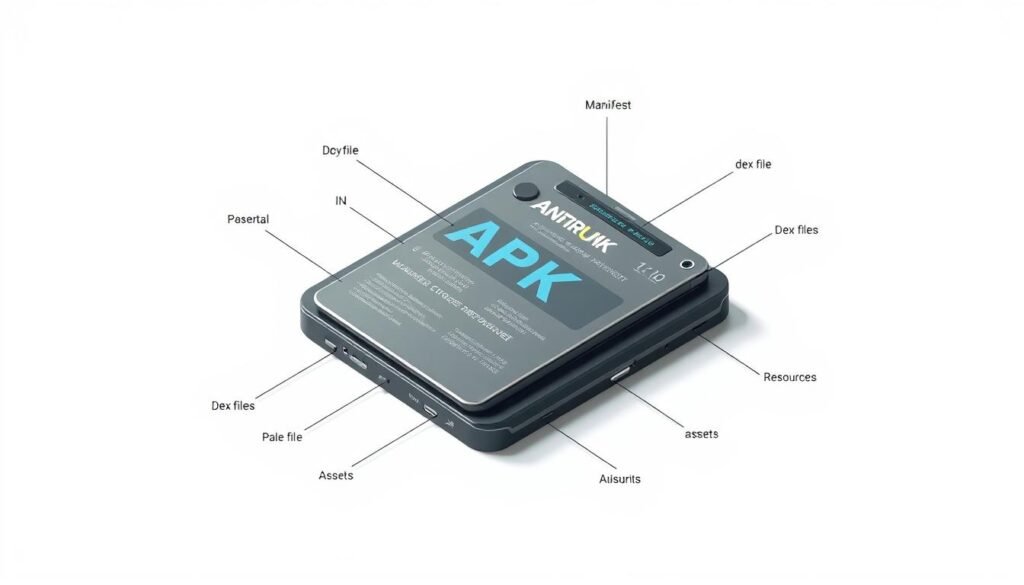
What is inside a standard install file?
An android package typically uses a ZIP backbone with a central directory and local file headers. Inside you’ll find compiled DEX code, resources, assets, signature metadata, and the critical AndroidManifest.xml.
That manifest lists components, supported Android versions, and requested permissions. Reviewing it early gives quick security insight into what the application might access on the system.
Why the manifest and headers matter for analysis
Static analysis begins by extracting files and reading the manifest. Most tools rely on consistent directory and header values to parse content. When headers mismatch, Apktool, Jadx, and common archive utilities often fail.
Some attackers tamper with local headers while leaving the central directory intact. Android’s installer trusts the central directory, so tampered apk files can still install even when tools error out.
| Tool | Typical behavior | When headers tamper |
|---|---|---|
| Apktool | Extracts and decodes manifest | Fails to read manifest |
| Jadx | Decompiles DEX into code | Errors during unpack |
| apkInspector | Parses and decodes manifests | Can recover manifests from tampered packages |
For defenders, knowing the package structure and format has clear value. Start by validating declared permissions and services. Unexpected permissions, odd directory entries, or failed tool runs are immediate red flags.
Tip: Prefer trusted stores and verified sources to reduce exposure to malformed files that masquerade as legitimate apps.
How Malicious APKs Reach Your Android Device
Attackers push repackaged app files through channels that look everyday—DMs, QR codes, and lure pages—so installs feel routine. This approach makes a harmful install seem normal and urgent, which lowers a user’s guard.

Distribution splits into two clear paths. The Google Play Store enforces policies and Play Protect scans apps for known malware and behavioral flags. That reduces exposure but does not catch every new variant.
By contrast, third-party sources and untrusted stores skip those checks. They host repackaged files and auto-download prompts. Threats arrive from phishing pages, brand-impersonating landing pages, and scam ads that mimic Facebook or TikTok.
- Attack vectors include DMs, messaging apps, QR codes, and off-market app stores.
- Social engineering themes use law-enforcement or “security protection” language to build trust.
- Users often accept install prompts because the app appears urgent or helpful.
Practical steps: check the publisher name and review history before installing. Organizations should restrict sideloading with MDM policies and allow only approved stores to limit exposure.
For deeper investigation into campaigns and indicators, read the Palo Alto case study on stolen PII and a checklist to validate app safety: campaign analysis and safety checks.
What Really Happens After Installation: From Permissions Abuse to C2
On first run, some repackaged files request extensive access and quietly contact remote servers for instructions. This initial handshake sets up persistence, remote control, and monetization paths without showing obvious signs to users.
Abusing permissions and background services: apps immediately ask for broad permissions to read contacts, media, location, and network state. They then spawn background services that restart on boot and listen for system events to stay active on the device.
Command-and-control bootstrapping: an installed file often fetches a Base64 payload, decodes it, then decrypts an AES-ECB blob using a hardcoded key. The decrypted config lists C2 URLs the application polls for code, tasks, and updates. That runtime updates model raises the long-term value of each infection because operators can change capabilities without sending a new installer.
Anti-analysis and sandbox checks: the application probes emulators and vendor images (for example, Genymotion signatures) and alters behavior to hide indicators during dynamic analysis. Some campaigns also subvert signature checks with tools like ApkSignatureKillerEx to load a secondary origin file and preserve a valid-looking facade.
| Post-install behavior | What to look for | Investigation clue |
|---|---|---|
| Permission escalation | Contacts, media, location requests | Unexpected permission changes in settings |
| C2 config retrieval | Base64 fetch + AES-ECB decrypt | Cached config files in app directory |
| Traffic monetization | Redirects, simulated ad clicks | Repeated outbound HTTP redirects to affiliate domains |
| Persistence | Background services restart on boot | Services listed in manifest and dropped files |
Practical detection tips: monitor system network calls, watch for sudden permission grants, and collect dropped files and directory artifacts for analysis. For related phone-billing schemes, see the toll-fraud case study at Microsoft for specific indicators and impacts: toll-fraud case study.
Categories of Malicious APKs Seen in the Wild
A concise taxonomy helps defenders spot patterns fast. Below are common categories found in real-world files and samples, with practical cues for quick analysis.

Ad fraud and traffic inflation
A single file can fake impressions and clicks to monetize traffic without real user value. These apps route requests through chained domains and simulated browsers, then load legitimate content to hide the scheme.
Credential stealers
Some apps present realistic login pages that mimic banks or social platforms. They capture credentials and exfiltrate information silently to remote services for later abuse.
Background data harvesters
These samples request broad permissions to read contacts, call logs, media, and device identifiers. They run minimal UI and send aggregated data back to operator servers.
Task reward and gambling apps
Task reward apps promise payouts but embed dark patterns and unreachable redemption. Gambling and betting apps push transactions in legal gray zones and harvest payment info or trigger risky charges.
- Runtime adaptability: many files toggle features by locale, language, or virtualization checks.
- Analysis tip: compare declared permissions versus the app’s stated function; mismatches are strong indicators of hidden behavior.
- Sampling: analyze multiple variants—shared code and services often reveal common infrastructure.
Technical Deep Dive: BadPack APKs and Anti-Analysis Tricks
BadPack samples corrupt ZIP headers so analysis tools break while the operating system still accepts and installs the file. This gap lets attackers hide the AndroidManifest.xml and delay triage, giving campaigns more time to run.
How ZIP structure and header mismatches work
The APK format is a ZIP container with a central directory and per-file local headers. Both must agree on compression method, sizes, and offsets for reliable extraction.
BadPack introduces deliberate mismatches between the local header and the central directory. That prevents common tools from locating and decoding the manifest and other critical files.
Why common tools fail
Typical failure messages include “Invalid CEN header” from Apktool, “unsupported compression method” from Jadx, and “Headers Error” from 7-Zip. JAR, unzip, and apksigner also choke when manifest reads fail.
Despite these errors, the Android runtime reads the central directory and can infer enough to install the file on an android device. That difference is the method’s strategic value to operators.
Attacker methods and recovery
- Wrong compressed sizes for STORE entries.
- Non-DEFLATE compression values when payloads are STORE.
- Altering only local headers while keeping DEFLATE payloads intact.
These methods waste analyst time, reduce automated coverage, and obscure harmful content. For recovery, restore header values or run apkInspector to extract and decode AndroidManifest.xml. Directory and file metadata remain forensic anchors; reconstructing them enables downstream static analysis and attribution.
Actionable tip: document samples and header anomalies across the campaign. Correlating repeated header tampering helps link infrastructure, tools, and operator behavior for faster detection and response.
Real-World Campaigns: Brand Impersonation and Modular Backends
These campaigns blend convincing brand look-and-feel with modular server architectures to scale theft and ad-fraud operations. They rely on staged config files and runtime updates so operators can change behavior after an install.
Spoofed Facebook/TikTok apps reuse official assets and a familiar UI to lower user suspicion. On launch, a delivered file may request broad permissions, then fetch a Base64, AES-ECB encrypted config from object storage. Decrypting that config reveals multiple C2 endpoints (for example, fbc003.txt–fbc039.txt) hosted across segmented subdomains like apk.kodownapp[.]top and tk.kodownapp[.]top.
The payload often uses signature-subversion tools such as ApkSignatureKillerEx to inject a secondary payload (origin.apk). That method makes the app appear properly signed to the Android system while loading hidden code and services.
Operators add sandbox checks (Genymotion detection) so behavior changes under analysis. They also use a fallback telemetry channel that looks like crash reporting — a simple HTTP endpoint that captures locale, platform, version, timestamp, and device metadata. That endpoint can act as a backup C2 if primary methods fail.
- Indicators: staged config files (fbc003.txt–fbc039.txt) and repeated connections to kodownapp subdomains.
- Attribution clues: Simplified Chinese strings (e.g., 用户信息为空) and China-hosted infrastructure — informative but not definitive.
- Defender actions: track code reuse, method names, and config formats across apk samples; block known domains and monitor repeated outbound connections.
Value to operators: combined ad-fraud and credential-theft capabilities, runtime adaptability, and low detection footprint make these campaigns high-value targets for attackers and a clear priority for defenders.
Malicious APK Risks for Users and Organizations
Scams that pose as law enforcement or “security protection” tools can turn a routine install into immediate financial harm. These schemes pressure users to install a file and hand over sensitive information under threat of legal action.
How the scam works: victims receive a warning that they are under investigation and are urged to install a “安全防护” app. The app asks users to select their bank and enter personal and banking details.
Permissions abused: requests like android.permission.CALL_PHONE and android.permission.RECEIVE_SMS let the app become the default phone and SMS handler. That lets it disconnect calls and suppress bank alerts so fraud can proceed unnoticed.
- Fraud flow: user installs the file, grants handlers, inputs banking info, then attackers drain accounts while alerts are blocked.
- Network indicators: repeated HTTP calls to
52.221.181.208andlog.tbs.qq.com, plus endpoints like/api/GetCmd.aspxand/api/getconfig.aspx. - IoCs to block: sample hashes such as
2cf117abf5ce…and IPs13.250.172.152,18.143.192.34,18.166.72.58,52.221.181.208.
User impact: financial loss, identity theft, and long recovery cycles are common when early alerts are suppressed. Even one compromised device can expose business email, messaging, and stored credentials for a small company.
Immediate response: isolate the device, preserve the file and logs, capture the sample for analysis, and engage professional incident response. Train users to distrust urgent install requests and verify official notices through separate channels. For deeper technical context, see this analysis on unmasking malicious files: unmasking malicious files.
Detection, Prevention, and Incident Response
Detect and act fast: repeated outbound connections, sudden permission grants, and new services that restart on boot are common early signs. Use those signals to trigger triage and containment.
- Restrict sideloading with mobile device management (MDM) and enforce installation only from the Google Play store and Play Protect.
- Enable centralized checks: require publisher verification and block installers from unknown sources.
- Harden the fleet: raise minimum OS versions and maintain an allow-list for critical apps and services.
How do you train users effectively?
Teach quick verification steps. Ask users to check the publisher, avoid installs from links or QR codes, and review requested permissions before granting them.
Spot brand impersonation: mismatched icons, poor translations, or pressure to act immediately are red flags.
What should network detection monitor?
Tune sensors for repeated, rapid connections to legitimate domains that can act as command-and-control channels. For example, correlate hits to log.tbs.qq.com with recent installs or active processes.
Block known infrastructure such as 52.221.181.208 at the edge and feed those IoCs into DNS filtering and URL policies.
What are the incident response steps?
- Isolate the affected android device from the network.
- Collect the installation file, compute hashes, and preserve application install logs and directory artifacts.
- Capture network traces and process lists, then compare samples to known indicators.
- Revoke tokens and reset credentials tied to the device or account.
- Engage external incident response partners when needed and document the timeline for lessons learned.
| Control | Action | Value |
|---|---|---|
| MDM policy | Disable sideloading; enforce Play Store only | Reduces installs from untrusted sources |
| Network filtering | Block IPs (e.g., 52.221.181.208); monitor suspicious hostnames | Stops C2 beacons and reduces data exfiltration |
| Tools & analysis | Use apkInspector if Apktool/Jadx fail; attempt header repair | Recovers manifest and enables deeper analysis |
| IR playbooks | Standardize triage: sample capture, hash, log preservation | Speeds consistent incident response and reduces dwell time |
Post-incident hardening: enforce store-only installs, add DNS and TLS inspection where lawful, and measure mean time to detect and respond. These steps lower the long-term value attackers gain from a single compromised file and protect your users and business from wider harm.
Conclusion
Keep control of installs and watch runtime signals: simple policies and steady monitoring stop most attacks before damage starts.
Threat actors exploit trust and format quirks to turn a routine install into persistent access. Verify the publisher, prefer Google Play and Play Protect, and restrict installs from third-party sources.
Watch runtime indicators: inspect directory artifacts, file drops, repeated outbound connections, and odd behavior on the android device. Collect apk files and apk samples, preserve logs, and isolate affected devices for analysis.
Technical pillars to track include AES‑ECB configs, signature subversion, sandbox-aware code, and header tampering that breaks tools. Follow a clear incident response: isolate the device, gather files and samples, review logs, and escalate to responders.
With source verification, permission scrutiny, and layered tools, you reduce the value attackers gain from each file and keep apps trustworthy across your fleet.
FAQ
What really happens when you install a harmful APK on an Android device?
Installing a compromised Android package can grant the app broad capabilities defined in its manifest. It may request access to contacts, storage, SMS, camera, or accessibility services. Once granted, the app can exfiltrate data, intercept messages, perform background tasks, or contact remote servers for commands. Some packages drop additional payloads, modify system settings, or install persistent services that resist removal. Always review requested permissions and source before installing.
What is an Android Package (APK) and what files are inside it?
An APK is a signed ZIP archive that bundles an app’s compiled code (DEX files), resources (images, layouts), certificates, and the AndroidManifest.xml. The manifest lists permissions, components (activities, services, receivers), and intent filters. Understanding these contents helps you assess an app’s behavior before installation and during analysis.
Why does AndroidManifest.xml matter for security?
The AndroidManifest.xml declares what the app can do and what it needs. Permissions in the manifest indicate potential data access or device control. Exported components or intent filters can expose attack surfaces. Malicious authors sometimes over-request privileges or use privileged APIs; checking the manifest is a first line of defense.
How do compromised Android packages reach devices?
Threat actors use multiple delivery paths: third-party app stores and sideloading, phishing links, malicious QR codes, attachments in messaging apps, or repackaging legitimate apps. Some variants slip into the Google Play Store by evading automated checks. Social engineering and brand impersonation increase click-through rates.
How reliable is the Google Play Store and Play Protect at blocking threats?
Google Play and Play Protect catch many threats but are not perfect. Automated scans can miss well-obfuscated or novel techniques. Play Protect focuses on known indicators, while sophisticated payloads use packing, delayed activation, or server-side components to evade detection. Prefer Play-signed apps and keep Play Protect enabled as part of layered defense.
What social engineering techniques lure users into installing malicious packages?
Attackers impersonate trusted brands, create fake update prompts, or mimic popular apps’ UI. They use phishing pages, push notifications, and fake reviews to build trust. Deceptive reward or utility apps promise features or money to encourage sideloading. Always verify publisher identity and download source.
What are common post-install behaviors from harmful packages?
After installation, adversarial apps may abuse permissions to harvest contacts, SMS, media, and device identifiers. They commonly set up command-and-control (C2) channels to retrieve configuration or updates, perform ad fraud, redirect traffic, or execute payloads. Some implement encryption for configuration files and use runtime updates to change behavior.
How do attackers use permissions to abuse an Android device?
Attackers request permissions that enable surveillance or persistence: READ_CONTACTS, READ_SMS, RECEIVE_SMS, ACCESSIBILITY_SERVICE, and storage access. Accessibility permissions are particularly powerful—they can read screen content and perform input actions. By combining permissions, an app can intercept two-factor codes, manipulate apps, and exfiltrate sensitive data.
What is command-and-control (C2) behavior in these packages?
C2 involves the app contacting remote servers to fetch instructions, configuration, or additional payloads. Operators may use AES-encrypted configs, segmented subdomains, or fallback channels disguised as crash-reporting APIs. This model enables dynamic updates and modular feature changes without republishing the package.
How do harmful packages evade analysis and sandbox detection?
Evasion techniques include emulator checks, timing delays, debugger detection, encrypted resources, and integrity checks. Authors tamper with archive headers or use anti-decompilation tricks to break tools like Apktool or JADX. These behaviors delay analyst visibility and reduce the effectiveness of automated scanners.
What kinds of fraudulent behaviors do these apps perform to monetize compromise?
Common monetization tactics include ad fraud (inflating impressions/clicks), affiliate and redirect schemes, premium SMS billing, in-app purchase abuse, and credential theft for resale. Some apps operate gambling or betting functions in legal gray areas to launder funds or harvest payment data.
What categories of harmful apps are most seen in the wild?
Analysts frequently encounter ad-fraud apps, credential stealers targeting banks and social platforms, background harvesters collecting media and metadata, deceptive reward apps demanding excessive permissions, and unregulated gambling apps. Each category uses distinct techniques to blend in and persist.
Why do common analysis tools sometimes fail on tampered packages?
Some attackers deliberately corrupt ZIP headers or mismatch local and central directory entries to confuse unzip, 7-Zip, apksigner, and reverse-engineering tools. They may also strip or obfuscate signatures and resource tables so standard tooling errors out or produces partial outputs.
How can analysts recover a tampered package for inspection?
Recovery often requires repairing ZIP headers, rebuilding central directories, or using specialized inspectors that tolerate anomalies. Tools like apkInspector and forensic ZIP utilities can reconstruct manifests and extract DEX files. Analysts should work on copies and document every modification.
How do brand-impersonation campaigns operate in practice?
Attackers clone popular apps’ appearance, reuse logos, and craft fake UIs to mimic Facebook, TikTok, or banking apps. They subvert APK signatures, use lookalike package names, and push social-engineered installs via ads and phishing pages. Combined with credential phishing, this yields high credential capture rates.
What indicators help attribute modular backends or shared tooling?
Shared AES keys or ECB-mode configs, recurring subdomain patterns, identical telemetry endpoints, and code reuse across samples point to a common ecosystem. Language artifacts, such as Simplified Chinese strings or comments, and similar compile-time metadata can aid attribution but require corroboration.
What are the primary impacts on users and organizations?
Impacts range from privacy invasion and financial loss to fraud, unauthorized transfers, and credential theft. Organizations face data leakage, fraudulent transactions, and increased incident response costs. Blocking SMS or call alerts and intercepting MFA codes can enable account takeover.
What are key indicators of compromise (IOCs) for installed packages?
IOCs include unusual permissions requests, new background services, persistent processes, repeated outbound connections to strange domains, unexpected SMS activity, and unexplained data exfiltration. Collecting APK samples, network logs, and device snapshots helps confirm compromise.
How can users and admins prevent installations from risky sources?
Apply preventive controls: disable sideloading where possible, restrict installs to the Google Play Store, enable Play Protect, and use enterprise mobile management (EMM) for policies. Maintain OS and app updates, and configure app whitelists for sensitive devices.
What user practices reduce the chance of falling for impersonation and phishing?
Educate users to verify publisher names, check app signatures, read reviews critically, and avoid installing from links in messages. Inspect requested permissions and decline apps that ask for unrelated privileges. When in doubt, download directly from the official store or vendor site.
How can network monitoring detect compromised apps contacting C2 servers?
Look for repeated or periodic connections to unfamiliar domains, use DNS and TLS inspection to spot anomalies, and flag traffic patterns that mimic beaconing. Correlate device-level events with network telemetry to identify suspicious endpoints used for configuration or exfiltration.
What are the core incident response steps after detecting a compromised device?
Isolate the device from networks, preserve volatile logs, collect the APK sample and related artifacts, and capture network traces. Perform static and dynamic analysis in a controlled lab, update detection signatures, and engage legal or vendor support if financial fraud is suspected.
How should organizations handle APK sample sharing and analysis?
Share samples with trusted malware analysis platforms and CERTs using secure channels. Redact sensitive customer data and include metadata: hashes, timestamps, and network indicators. Follow disclosure policies and coordinate with endpoint security teams for containment.
What immediate protections help after an incident to prevent recurrence?
Patch systems, rotate compromised credentials, enforce multi-factor authentication using phishing-resistant methods, and roll out stricter app install policies. Conduct user training, update EDR/Mobile threat defense rules, and monitor for similar IOCs across fleet devices.
