Can small, overlooked signs really reveal origin of an intrusion?
This piece walks a past-tense, practical path through how artifacts, traffic, and metadata matched up into a clear outcome.
Analysts correlated malware behavior, packet captures, and host logs. Bits of data and tiny clues formed timelines. That set of activity made links visible.
Tools such as YARA, VirusTotal, Zeek, and MITRE ATT&CK guided phase mapping. Code strings, compiler timestamps, and reused C2 infrastructure gave context. Such correlation helped match suspects and motives without guesswork.
Every finding tied into security controls and documented information with time and source. Where public example matched artifacts, teams reproduced actions in a lab. This kept response fast and audit ready.
Key Takeaways
- Clear model speeds evidence collection and keeps work deliberate.
- Small clues — strings, timestamps, odd domains — often matter most.
- Multiple sources must validate any attribution.
- Preserve volatile data early to avoid losing key activity.
- Safe lab reproduction shortens response while confirming hypotheses.
Setting the Scene: Scope, Safety, and Legal Groundwork for a Forensic Hunt
Incident response started with a focused scoping session that named impacted systems, users, and risk limits. We prioritized safety and lawful authority before any capture.
Teams defined which systems and devices held potential evidence and who had lawful access. Leadership and counsel agreed containment boundaries. That step avoided over-collection and kept production availability intact.
Establishing chain of custody and preserving volatile evidence
- Record custody: log every handoff, timestamp, role, and reason.
- Capture order: volatile memory, live network sessions, then disk images with hashed copies.
- Mixed-use devices: schedule access windows and explain handling to users to protect privacy.
Coordinating with legal and, when appropriate, law enforcement agencies
Legal and compliance signed collection plans and retention rules. When cross-border or criminal elements existed, relevant agencies were briefed early so subpoenas or warrants could align with technical steps.
Mapping the Intrusion Against the Cyber Kill Chain
We aligned artifacts to each phase of the Cyber Kill Chain to keep the hunt structured. Mapping observed techniques to ATT&CK produced testable hypotheses and a lean collection plan.
Aligning stages revealed where evidence lived. Recon left open-source footprints and unusual queries. Delivery showed phishing headers and web payload URLs. Exploitation surfaced crash logs and EDR alerts. Installation appeared in new services, scheduled tasks, and registry run keys.
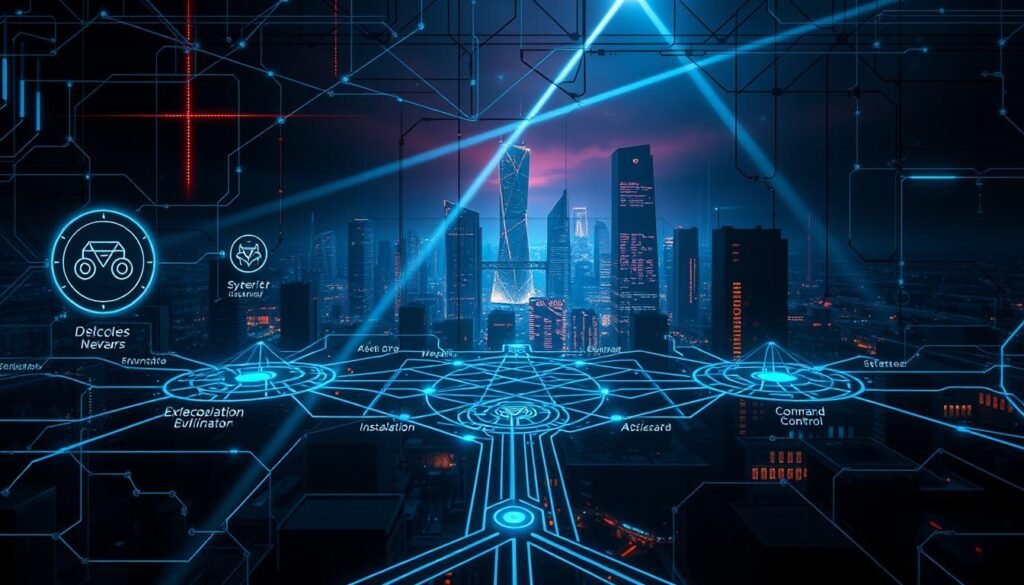
Recon through C2: Where each phase left clues
We tracked periodic beacons, odd DNS patterns, and TLS fingerprints to separate malicious traffic from normal network noise.
- Delivery: extract headers and URLs for blocking and sinkholing.
- Exploitation: follow parent-child process chains and crash traces.
- Persistence: date-stamp services and scheduled tasks for initial foothold.
- C2: hunt for periodic beacons and uncommon JA3/JA4 signatures.
Turning phases into hypotheses and collection priorities
Using ATT&CK, teams connected scattered observations into coherent techniques and methods. That mapping suggested where else to pull information — email gateways, browser caches, identity logs.
Outcome: prioritize hosts and networks most likely to contain clear events, reduce noise, and speed up response against known threats and unknown attacks.
Malware Is the First Footprint: Static and Dynamic Analysis
We began with the sample itself—pulling readable strings, hashes, and timestamps, then detonating it inside an isolated sandbox.
That quick pivot from static markers into live behavior let analysts build precise hypotheses and hunting queries.
Static markers that point at origin
Static analysis extracted readable strings that exposed candidate domains, file paths, and execution flags. Analysts captured MD5 and SHA256 hashes and collected build metadata for cross-reference with global repositories and internal data.
Dynamic runs that reveal actions
Sandbox detonations showed process trees, registry edits used for persistence, and exact files dropped or modified. Outbound DNS and HTTP(S) calls revealed servers used for first contact and fallback logic.
Linking traits to known campaigns
Pattern matching with YARA rules and VirusTotal searches clustered the sample with prior sightings. Code reuse, mutex names, and embedded library versions hinted at development timelines and shared code pools.
Outcome: each behavior finding fed EDR and SIEM hunting queries so teams could find other hosts touched by the same hacker toolkit and improve network detection.
Metadata Matters: Hidden Clues in Files, Emails, and Media
Metadata can reveal when, where, and who acted inside compromised systems. Short fields inside documents, binaries, and mail headers often point at time zones, user handles, and build tools.
Document headers and media EXIF can expose time-zone offsets and last-modified user names. Executable headers list compiler timestamps and build paths that matched prior campaign samples.
Email headers map relay paths and server hops, showing precise timestamps and IPs. Comparing those routes against gateway logs helped confirm first ingress points into our network.
- When fields were scrubbed: we examined MFT entries and .lnk artifacts to infer original creation and execution.
- For media found in exfil caches: EXIF and device tags sometimes survived obfuscation and gave location or model data.
- Real example: non‑Latin usernames and Eastern European offsets lined up with working‑hour patterns in known cases.
| Artifact | What it reveals | Action |
|---|---|---|
| Document properties | User name, time zone, last edit | Cross-check with account logs |
| Executable headers | Compiler, build time, paths | Match against known samples |
| Email headers | Relay servers, timestamps, IPs | Correlate with perimeter logs |
For deeper reading, see how metadata can speak about origin and intent.
Following Packets and Logs: Network Forensics and Timeline Correlation
Packet captures and multi-source logs built a minute-by-minute picture of intrusion activity. Analysts paired protocol inspection with telemetry so sequences of access and lateral moves became clear.
Packet inspection used Wireshark for deep protocol views. Broad telemetry came from Zeek and an ELK Stack deployment. Together, these tools flagged unusual outbound traffic, DNS tunneling, and encrypted C2 channels.
How traffic anomalies revealed covert channels
- Summary: Captured packets were inspected, then host and perimeter logs were stitched into a timeline. Beaconing and lateral moves appeared across systems and servers.
- Baseline egress profiling surfaced rare domains and steady-interval calls that suggested covert channels.
- DNS logs showed data-length spikes and high-entropy subdomains; sample streams were decoded for validation.
- PCAPs provided TLS handshake details and JA3/JA4 hashes to separate benign clients from suspicious beacons.
Correlating multi-system logs
Zeek notices and ELK visualizations highlighted authentication spikes and odd SMB or RDP access. Event IDs and timestamps from Windows and Linux endpoints were aligned on a single clock. That placed each step—initial foothold, escalation, lateral jump—on a shared timeline.
From endpoints toward containment
Mapping host-to-host jumps revealed segmentation failures and ideal chokepoints for containment. Every domain, IP, and URI path fed blocklists and detection rules while care was taken not to disrupt business flows during mitigation.
From Indicators to Attribution: the forensic trail we followed to trace a hacker
We consolidated IOCs and mapped observations against ATT&CK, then validated overlaps with public and private intelligence.
Infrastructure reuse and work‑hour patterns strengthened attribution confidence while remaining cautious.
Building an IOC set: hashes, IPs, domains, paths, and scripts
Our IOC set combined host and network artifacts. It included file hashes, mutex names, service strings, domains, IP addresses, and script fragments pulled from droppers and loaders.
Each indicator was timestamped, hashed, and stored in a sharing platform for enrichment.
Comparing TTPs with MITRE ATT&CK and threat intelligence
Analysts mapped persistence, lateral movement, and credential access techniques against ATT&CK entries. That mapping highlighted likely follow-on steps and detectable signals.
- Cross-checks: MISP, VirusTotal, and vendor reports revealed overlaps with prior campaigns.
- Validation: hosting timelines and SSL reuse were matched against our event window before linkage was accepted.
Case-in-point patterns: APT reuse of infrastructure and business‑hour clues
In one instance, reused C2 servers, Cyrillic locale settings, and Moscow business‑hour compiler timestamps aligned with known APT activity linked to APT28 (Fancy Bear).
Attribution remained probabilistic; analysts treated language and timestamps as weak signals unless corroborated by infrastructure and tooling matches.
| Indicator | What it suggested | Action |
|---|---|---|
| File hash | Exact sample match in repositories | Block and hunt across endpoints |
| Domain/IP | Repeat hosting with prior campaigns | Sinkhole, blacklist, and timeline check |
| Compiler timestamps / locale | Work‑hour patterns and language hints | Use as corroborating evidence only |
| Script fragments / mutex | Tooling fingerprint and persistence | Create YARA and detection rules |
Outcome: this process produced actionable guidance for security teams and a concise, qualified report for leadership about likely origin and intent.
Turning Insight into Defense: Tools, Techniques, and Ongoing Detection
Operational teams codified lessons into runnable detections and repeatable playbooks. They pushed queries into SIEM, spun up Zeek sensors, and shared indicators through MISP.
That work moved findings from analysis into active protection. Playbooks aligned detection with containment, and deception increased early warning.
Which technologies and sensors did teams deploy?
SIEM rules, ELK pipelines, and MISP sharing formed a core operational stack.
- SIEM: rules for beacon intervals, parent-child anomalies, and PowerShell abuse.
- Zeek/ELK: long-term network context that exposes technique shifts across networks.
- Wireshark: deep packet inspection for validating alerts and dissecting odd traffic.
- MISP: collaborate and enrich IOC sets and timeline data.
How did deception and hardening raise cost for attackers?
Honeypots and honeytokens were placed inside repos and file shares. Alerting from those traps gave early signals and caught lateral access attempts.
What limits remained and how were they managed?
Anonymous proxies, strong encryption, and cross-border law limits complicated attribution. Teams leaned on endpoint telemetry, certificate pin checks, and legal coordination. AI/ML helped spot patterns, while blockchain was explored for evidence integrity and cryptocurrency tracing.
Outcome: detections, hardened controls, and ongoing sharing turned insight into resilient cyber defense for systems, devices, and data.
Conclusion
Closing an investigation meant turning findings into clear playbooks and repeatable checks. That shift kept evidence handling auditable and detection practical across every system you manage.
Final work translated malware analysis, metadata review, and packet inspection into runnable rules and runbooks. Teams tested detections against realistic attack paths and validated software inventories.
Good practice layers multiple weak signals — code traits, work‑hour patterns, and reused infrastructure — until confident links emerge.
Invest in repeatable workflows, train users on phishing, and keep documentation tidy so digital forensics can scale and support agencies or court requests. Read more about real dark‑web paths and recovery steps in this digital forensics perspective.
